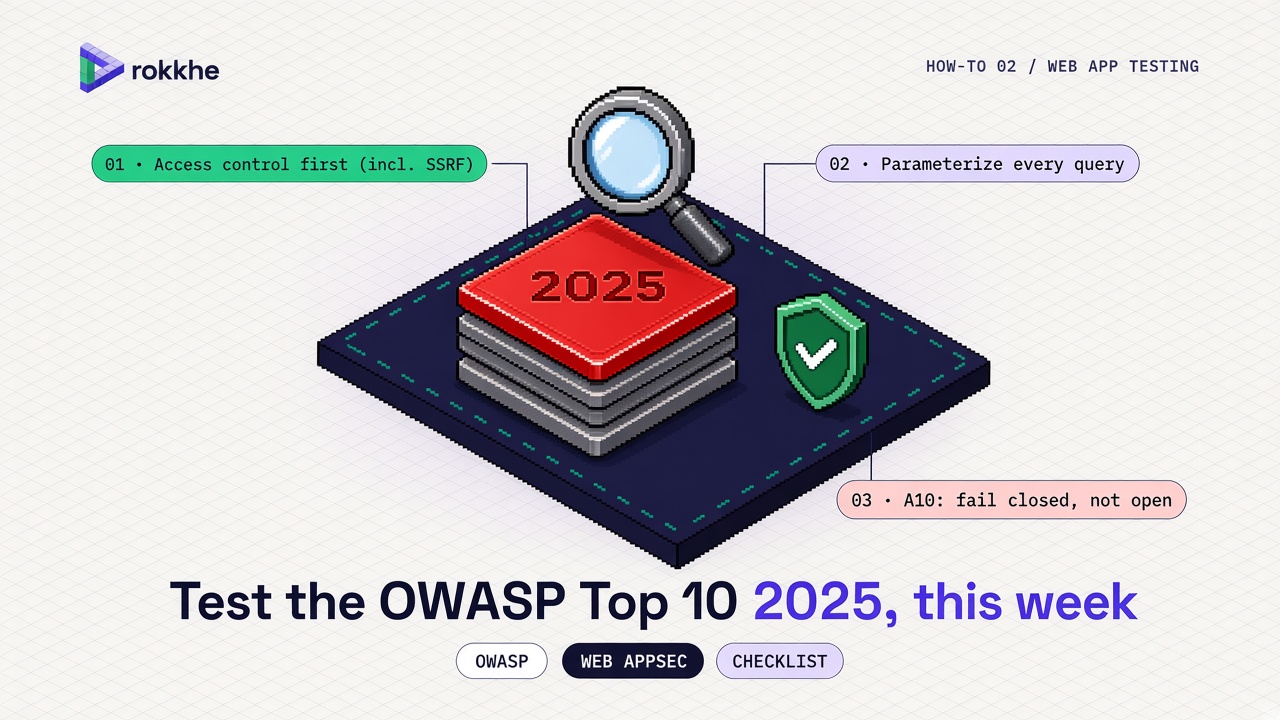
Test and fix the OWASP Top 10 2025 in your web app this week
A hands-on pass of the 2025 list: access control first, then configuration, injection, authentication, logging and exceptional conditions.
A hands-on pass of the 2025 list: access control first, then configuration, injection, authentication, logging and exceptional conditions.
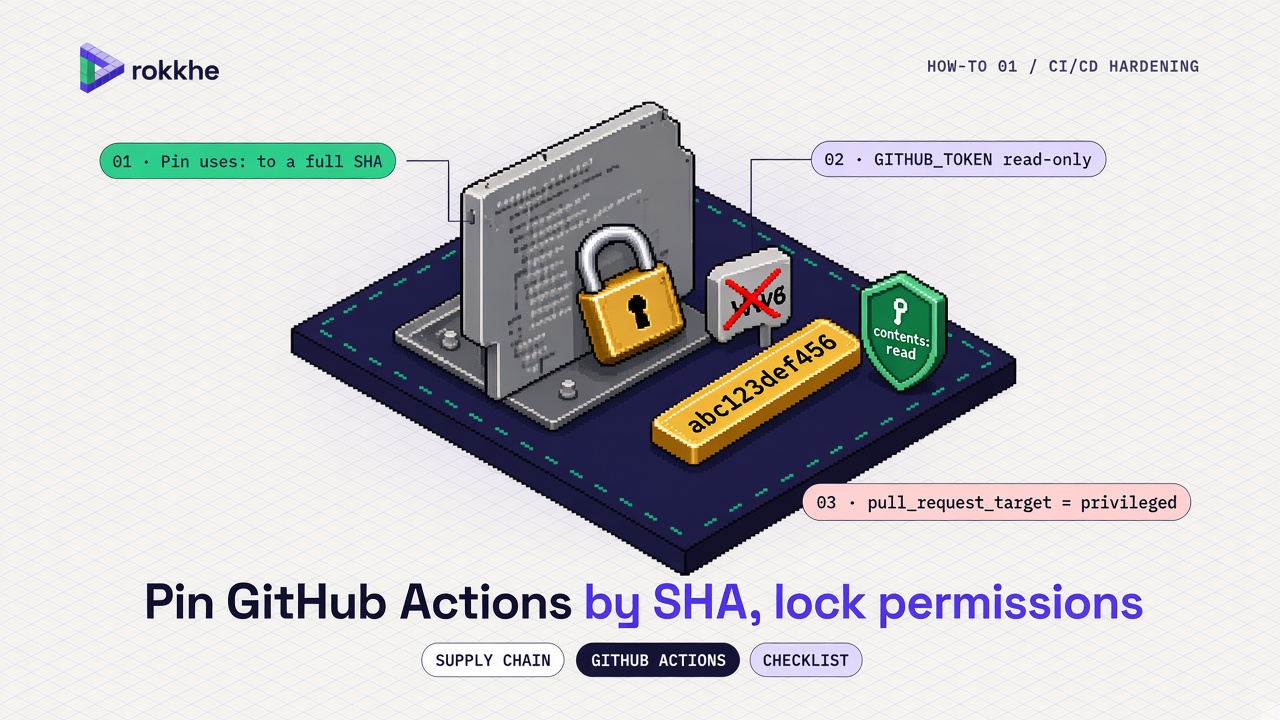
Replace movable tags with a 40-character SHA, set GITHUB_TOKEN to read-only by default, and treat pull_request_target as a privileged event.
Vulnerability briefing · 13 November 2026 · By the Rokkhe research team CVE-2026-123039 is a high-severity (CVSS 7.8) privilege escalation in the DynamicCLI service of Check Point Gaia OS. On 12 Novem